SecurityEndpoints & devicesNote
N-able ships its N-central fix as exposed servers fall from 1,338 to about 148
N-able’s release notes, status page and CVE records of 10 and 11 November: what Hotfix 2 fixes, what it switches off, and what a managed service provider does next.

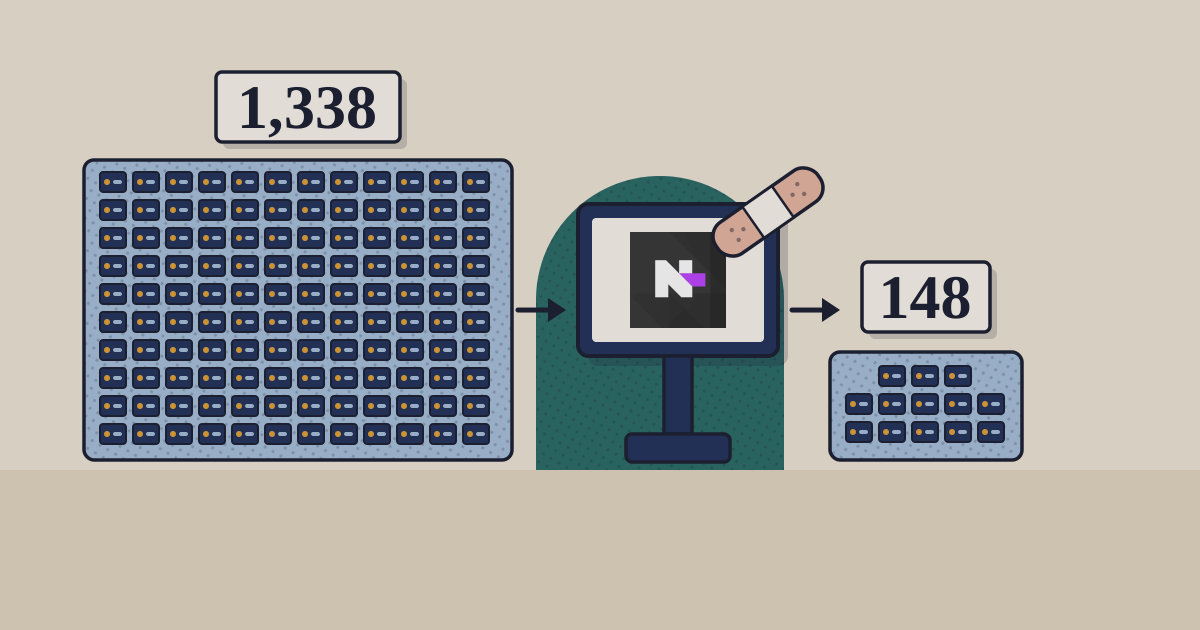
N-able released N-central 2026.4 Hotfix 2 late on 10 November, about 41 hours after a researcher published 33 exploits for its remote-management software, and by 01:04 UTC on 11 November it had upgraded every hosted server in all regions.12 On-premises servers are the customers’ job. Shadowserver, a non-profit that scans the internet, counted 1,338 N-central servers reachable online on Monday 9 November and just over 148 on 11 November, BleepingComputer reported.4
1,338
N-central servers reachable online on 9 November
Shadowserver, via BleepingComputer
~148
reachable on 11 November
Shadowserver, via BleepingComputer
7
CVEs fixed in Hotfix 2; two are entries for several bugs
N-able release notes
2
of the seven rated critical, both reachable without a login
CVE records, CVSS 4.0
01What the fix covers, and what it leaves for later
The hotfix, build 2026.4.1.26, lists seven CVEs. Two are labelled as several flaws at once: “Multiple XXE Vulnerabilities”, the XML class behind the researcher’s most serious chain, and “Multiple OGNL Injection vulnerabilities”.1 The XXE entry and a server-side request forgery in service import both score 9.3 and need no login; the rest need a login, an administrator’s rights or local access, and score 8.3 to 8.7.3 N-able calls it the release “addressing the most critical November 9 vulnerabilities” and says “a follow-up hotfix will be released to provide further security updates”.2
The release also removes legacy mobile device management and switches off N-central’s built-in remote control, which “will be re-enabled in a future fix”; Take Control, N-able’s separate remote-access tool, keeps working.1 Defused, a threat-intelligence company, said on 10 November it had seen probes opening anonymous agent sessions, pulling appliance configuration and “hitting the remote control endpoint without auth”.4 N-able reports scanning tied to the published code; neither it nor CISA’s list of exploited flaws records an attack on a customer.26
Hosted servers were upgraded about 45 hours after the exploits went public
N-central events, 9 to 11 November 2026, in UTC
Show tableHide table
| Date | Event | Detail |
|---|---|---|
| 9 Nov, 04:14 UTC | 33 exploits published | Able2Shell repository on GitHub |
| 9 Nov, 14:00 UTC | Hosted N-central offline | On-premises customers told to switch servers off |
| 10 Nov, 20:48 UTC | Hotfix 2 release notes | Build 2026.4.1.26 |
| 10 Nov, 21:19 UTC | Seven CVEs published | 21:19 to 21:26 UTC |
| 11 Nov, 01:04 UTC | All hosted servers upgraded | |
| 11 Nov, 12:32 UTC | About 148 servers reachable | Shadowserver, as reported |
Source: Researcher's repository; N-able release notes and status page; CVE records; BleepingComputer · as of 11 November 2026 · The last event is the time BleepingComputer published the count
02What a managed service provider should do now
Upgrade the server before bringing it back online: N-able still advises keeping on-premises servers off “until your server has been successfully upgraded”. Versions from 2025.4 upgrade directly; anything older must first move to a supported build.12 Then upgrade agents and probes, which both hosted and on-premises customers must do themselves, agents first: a probe on the new build cannot talk to an older agent, and features such as the offline patch cache stop until both match.1 Plan for remote sessions to run through Take Control until built-in remote control returns.
The background, including why one console reaches every customer, is in our Note of 10 November, N-able takes N-central offline worldwide after 33 exploits go public.
Sources
- N-able, N-central 2026.4 HF2 Release Notes (build 2026.4.1.26) — 10 November 2026
- N-able, status page: N-central Critical Security Incident, Release Available (event 202584) — update of 11 November 2026, 01:04 UTC
- CVE Program, records CVE-2026-125878 to CVE-2026-125883 and CVE-2026-91000 (N-able as CNA) — 10 November 2026
- BleepingComputer, N-able releases security hotfixes for zero-day vulnerabilities — 11 November 2026
- N-able, N-central Security Update (first published 6 August, updated 10 August) — 10 August 2026
- CISA, Known Exploited Vulnerabilities catalogue (N-able entries) — as released 10 November 2026
Disclosure. TechBag is a software reseller: it earns a margin when a reader buys through it, including from vendors named here. The analysis is TechBag’s own; no vendor paid for or saw this piece before publication. Facts are labelled reported, TechBag count or our view.
Keep reading