SecurityThreats & vulnerabilitiesNote
Two hijacked releases of Microsoft’s agent-framework stole Azure and CI tokens
Wiz’s, OX Security’s and Endor Labs’ analyses of 17 and 18 November: how releases 1.26.1 and 1.26.2 ran on every Python start, what they took, and what to rotate.

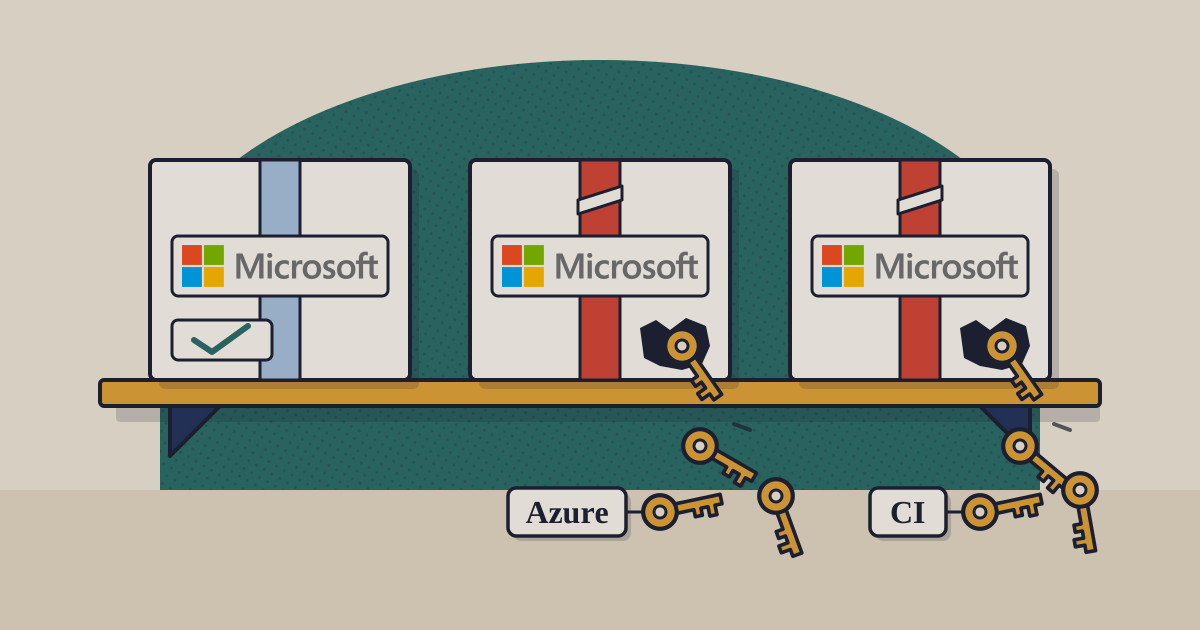
Two releases of Microsoft’s official agent-framework package on PyPI, versions 1.26.1 and 1.26.2, carried a credential stealer. The first went up at 20:35 UTC on 17 November (2:05am IST on 18 November), the second 33 minutes later, and both were gone from PyPI by 21:30 UTC.1 The package is Microsoft’s kit for building AI agents in Python. OX Security counts 192,534 downloads a month; Wiz puts it at about 41,000 a week.21 The last clean release is 1.26.0, published on 12 November.4
01Installed, never imported
The stealer did not wait for anyone to use the framework. Each release dropped a .pth file into the root of site-packages, and Python runs those on every interpreter start, so any Python process in that environment ran the payload even if it never imported agent-framework.1 Both releases pulled in the genuine agent-framework-core 1.26.0, so applications kept working normally.2 Only the meta-package was touched: the 22 sibling packages Endor Labs checked still showed 12 November as their latest release.3
It was aimed at the machines that build and run agents. It collected secret-looking environment variables; up to 60 credential files, including Azure CLI sessions, Git, Docker and Hugging Face tokens; Azure DevOps pipeline tokens; and Azure managed-identity tokens for 12 resources, Key Vault and Storage among them. All of it went in one compressed POST to a public request-inspection service, webhook.site.1 Version 1.26.2 moved the payload to a new file, so a search for 1.26.1’s file names misses it, and added GitHub Actions: in workflows allowed to request identity tokens, it asked for tokens that a federated credential in Entra ID can exchange for Azure access without any stored secret.13
The two hijacked releases were on PyPI for under an hour
agent-framework releases and disclosures, 12 to 18 November 2026, in UTC (IST in each detail)
Show tableHide table
| Date | Event | Detail |
|---|---|---|
| 12 Nov, 18:25 UTC | Clean 1.26.0 released | Wheel and source; 11:55pm IST |
| 17 Nov, 20:35 UTC | Malicious 1.26.1 | Stealer runs on every Python start; 2:05am IST, 18 Nov |
| 17 Nov, 21:08 UTC | Malicious 1.26.2 | Payload moved, GitHub Actions added; 2:38am IST |
| 17 Nov, 21:30 UTC | Both gone from PyPI | As Wiz observed it; 3:00am IST |
| 18 Nov, 14:00 UTC | 3 victims’ data found | Wiz, from the 50 stored requests; 7:30pm IST |
| 18 Nov, 17:23 UTC | Microsoft statement | Some repositories made private; 10:53pm IST |
Source: Wiz Research (17 and 18 November); PyPI release history; Microsoft as quoted by The Register · as of 19 November 2026, 11:30pm IST
02Microsoft’s own release key
Wiz says the attacker appears to have obtained a client certificate and private key for Microsoft’s Engineering System Release Pipeline (ESRP), the internal service that signs and publishes this package. A first attempt to publish from AWS was rejected by ESRP’s IP filtering; a second, from Microsoft-owned IP space, went through. How the credentials were obtained is not known.1 The attacker’s tooling reported its own progress to the same webhook it used for the stolen data, which let Wiz watch part of the operation.1
Nothing in the package metadata gave the releases away: author, links and description were copied unchanged. The tell was how they were cut. Neither shipped a source distribution, where every release from 1.21.0 to 1.26.0 had one, and no matching release appeared in Microsoft’s repository. PyPI showed no provenance attestation for either, but 1.26.0 had none either, so a user had no cryptographic way to tell them apart.3 “We have made some repositories private while we investigate malicious content,” a Microsoft spokesperson told The Register on 18 November.5 Microsoft has not said how many customers installed the releases.
03What a team that installed it should do
The theft had a ceiling the attacker chose. An unclaimed webhook.site address accepts at most 100 requests; Wiz confirmed this one was on the free tier and read the 50 requests it had stored. Four came from the attacker’s own machines and 29 from sandboxes, vendor scanners and tests; the other 17 were three distinct cases of victim data sent successfully.1 Those can still hold working cloud, build and registry keys.
Build pipelines have been the target all month: 4,837 hijacked GitHub accounts were used to steal CI secrets, and keys handed to an AI vendor opened the way to 149,346 Uber drivers’ data.
Sources
- Wiz Research, Microsoft agent-framework Compromised: Credential Stealer Targets Azure and CI Pipelines — 17 November 2026, 22:03 UTC; updated 18 November 14:00 UTC
- OX Security, Hijacked Releases of Microsoft’s Official agent-framework Steals Azure and CI Credentials — 17 November 2026, 21:50 UTC
- Endor Labs, agent-framework compromised: Python startup hooks steal Azure and CI credentials — 17 November 2026
- PyPI, agent-framework release history (JSON API) — 1.26.0 published 12 November 2026, 18:25 UTC; read 19 November 2026
- The Register, Microsoft’s official Python agent framework hijacked to distribute malware — 18 November 2026, 17:23 UTC
Disclosure. TechBag is a software reseller: it earns when companies buy through it, including from vendors named here. The analysis is TechBag’s own; no vendor paid for or saw this piece before publication. Facts are labelled reported, TechBag count or our view.
Keep reading