Data & privacyNote
Samyang fined ₩552m: a server left online after a migration leaked 149,767 people’s data
South Korea’s privacy regulator’s decision of 11 November: how a file server kept online after a data migration leaked 1.3TB, and what each of four Samyang companies was fined.

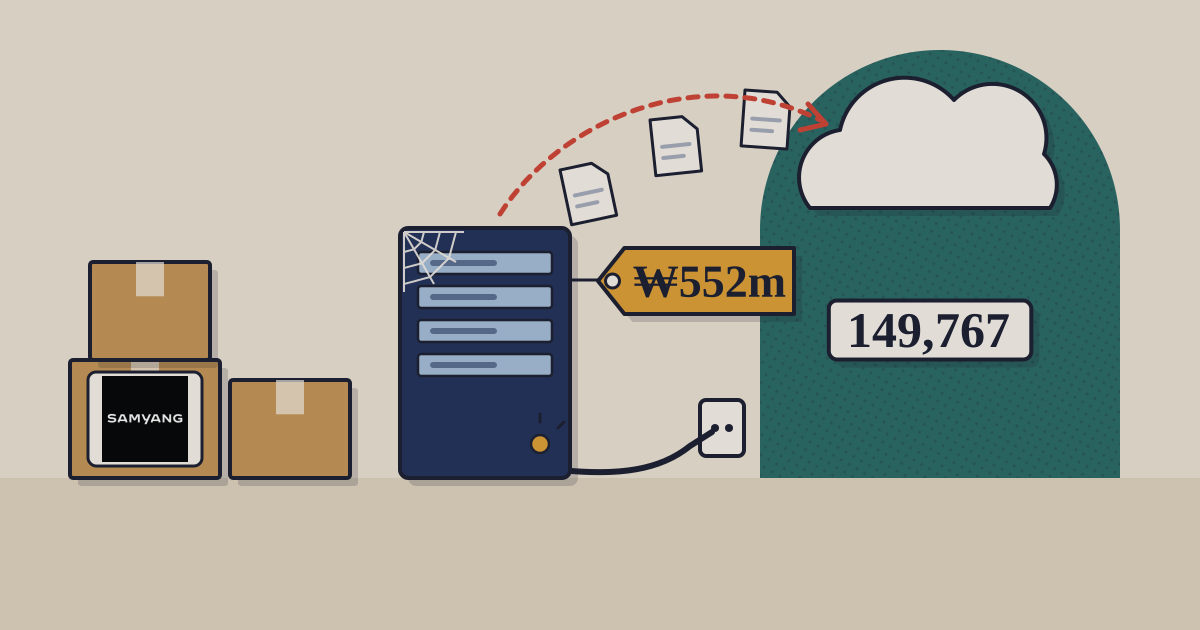
South Korea’s privacy regulator has fined three Samyang group companies ₩552m, ₩184m each, because a file server set up to move their data was left connected to the internet after the move was finished. In July 2022 an intruder used it to take about 850,000 files, 1.3TB, holding the personal data of 149,767 people, 82,750 of them with their resident registration numbers.1 The Personal Information Protection Commission decided the case at its plenary meeting on 11 November and published it on 12 November. It added ₩16.2m in smaller administrative fines, ordered corrections and ordered the decision made public.1
149,767
people whose data was taken: employees, shareholders and other contacts
PIPC
82,750
of them with their resident registration number, stored unencrypted
PIPC
1.3TB
about 850,000 files copied to an outside cloud
PIPC
₩552m
fines on three companies, plus ₩16.2m in administrative fines
PIPC
01How a finished migration became the way out
The four companies are Samyang Holdings, the group’s holding company; Samyang Corporation, which makes sugar and flour; Samyang Packaging, a plastic-packaging maker; and Samyang Data System, the group’s IT company, which handled their personal data for them.1 According to the PIPC, an unidentified intruder used a flaw in a group mail server to gain administrator rights, then stole the login details of an internal file server that had been installed to migrate data. Samyang Data System had left that server able to talk to outside networks from the end of the migration until the attack, which let the intruder move the three companies’ files to an external cloud “in a short period”.1
The PIPC found three more failures that made the damage larger. None of the three companies encrypted resident registration numbers, Korea’s lifelong national ID numbers. Samyang Holdings and Samyang Packaging kept day labourers’ pay records past their legal retention period. Samyang Holdings collected resident registration numbers when hiring without a legal basis. And when the leak happened, the three were already having Samyang Data System process their personal data without a written contract; they drew one up only in December 2024.1
The fine came four years and four months after the leak
Samyang group leak and the regulator's decision, by month, July 2022 to November 2026
Show tableHide table
| Date | Event | Detail |
|---|---|---|
| Jul 2022 | Files taken | 149,767 people's data from a migration file server left online |
| Dec 2024 | Contract written | the three companies' processing contract with Samyang Data System |
| Nov 2026 | Fines decided | ₩552m in fines and ₩16.2m in administrative fines, published 12 November |
Source: Personal Information Protection Commission, press release of 12 November 2026 · as of 12 November 2026
02Who paid what, and what to check after a migration
Each of the three companies was fined ₩184m and ₩1.8m for the unencrypted numbers and the missing contract. Samyang Holdings and Samyang Packaging were each fined ₩3.6m for keeping data too long, and Samyang Holdings ₩3.6m more for the hiring numbers. Samyang Data System received a corrective order.1 The PIPC’s advice is short: retire servers that are no longer used or cut them off from outside access, and delete personal data once it is no longer needed.1
At the same meeting the PIPC fined eight budget mobile carriers, including kt M mobile, LG HelloVision and KB Liiv Mobile, ₩171.3m in all. Four of them kept resident registration numbers, card numbers or bank account numbers in plain text.2
Sources
- Personal Information Protection Commission, 개인정보위, 안전조치 의무 위반한 삼양그룹 소속 4개사 제재 (four Samyang group companies sanctioned for breaching safeguard duties) — 12 November 2026 In Korean; decisions of the 22nd plenary meeting, 11 November.
- Personal Information Protection Commission, 개인정보위, 8개 알뜰폰 사업자의 개인정보 처리에 대한 조사 결과 발표 (results of the investigation of eight budget mobile carriers) — 12 November 2026 In Korean.
Disclosure. TechBag is a software reseller: it earns when companies buy through it, including from vendors named here. The analysis is TechBag’s own; no vendor paid for or saw this piece before publication. Facts are labelled reported, TechBag count or our view.
Keep reading